Security built into ICHRA operations

Responsible handling of sensitive information is part of everyday benefits administration. Security controls and documented processes help keep that handling consistent, developed around applicable HIPAA requirements.

Protection across the ICHRA process

ICHRA workflows involve employer, employee, enrollment, coverage, and payment-related information that requires consistent protection.


Different parts of that process carry different risks, and the controls below apply at the points where each one arises.
Protection across the ICHRA process

Security and access controls

Protected access

Role-based permissions limit platform access according to each user’s assigned responsibilities.

Secure authentication

Authentication and session controls protect user accounts and reduce the likelihood of unauthorized access.

Encrypted data

Sensitive information is encrypted during transmission and while stored.

Activity records

Administrative actions are logged with relevant user and timing information to support internal review and accountability.

HIPAA-aligned operations

Policies, procedures, and platform safeguards are developed around responsibilities for handling protected health information.

Secure infrastructure

The platform operates on modern cloud infrastructure selected for security, reliability, and scalability.

Protected access

Role-based permissions limit platform access according to each user’s assigned responsibilities.

Secure authentication

Authentication and session controls protect user accounts and reduce the likelihood of unauthorized access.

Encrypted data

Sensitive information is encrypted during transmission and while stored.

Activity records

Administrative actions are logged with relevant user and timing information to support internal review and accountability.

HIPAA-aligned operations

Policies, procedures, and platform safeguards are developed around responsibilities for handling protected health information.

Secure infrastructure

The platform operates on modern cloud infrastructure selected for security, reliability, and scalability.

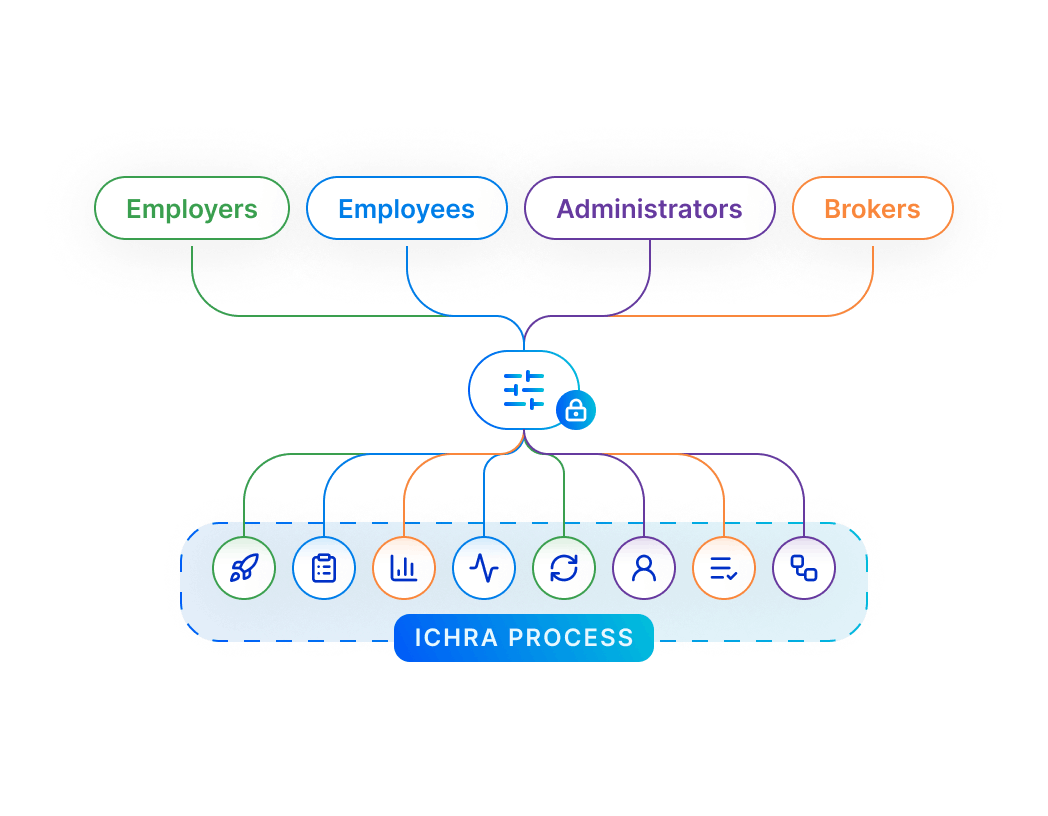
Access based on responsibility

Employers, brokers, employees, and platform administrators interact with different parts of the ICHRA process. Permissions are assigned according to each user’s role, keeping information and platform capabilities aligned with individual responsibilities while reducing unnecessary exposure.

Access based responsibility illustration

Security as an everyday practice

Security is not defined by a single feature, policy, or document. It depends on how information is accessed, transmitted, stored, reviewed, and handled day to day.

No platform can eliminate every potential security or privacy risk. Lirvion addresses that reality through layered technical controls, documented procedures, regular review, and clearly defined roles across the organizations and users involved.

Security as an 
everyday practice

A shared responsibility

Lirvion provides the technology and operational framework for the responsible handling of sensitive benefits information.

Protecting that information also depends on employers, brokers, administrators, employees, and service partners following appropriate security practices and managing access responsibly.

As the platform evolves, its controls and supporting safeguards will continue to be reviewed and strengthened.

A shared 
responsibility

Ready to run ICHRA with confidence?

One infrastructure layer powering ICHRA operations